Version: v3.4 
Security Findings
The Security Findings section provides detailed information about security issues, vulnerabilities, and compliance violations with comprehensive management capabilities for tracking and resolution.
Findings Overview
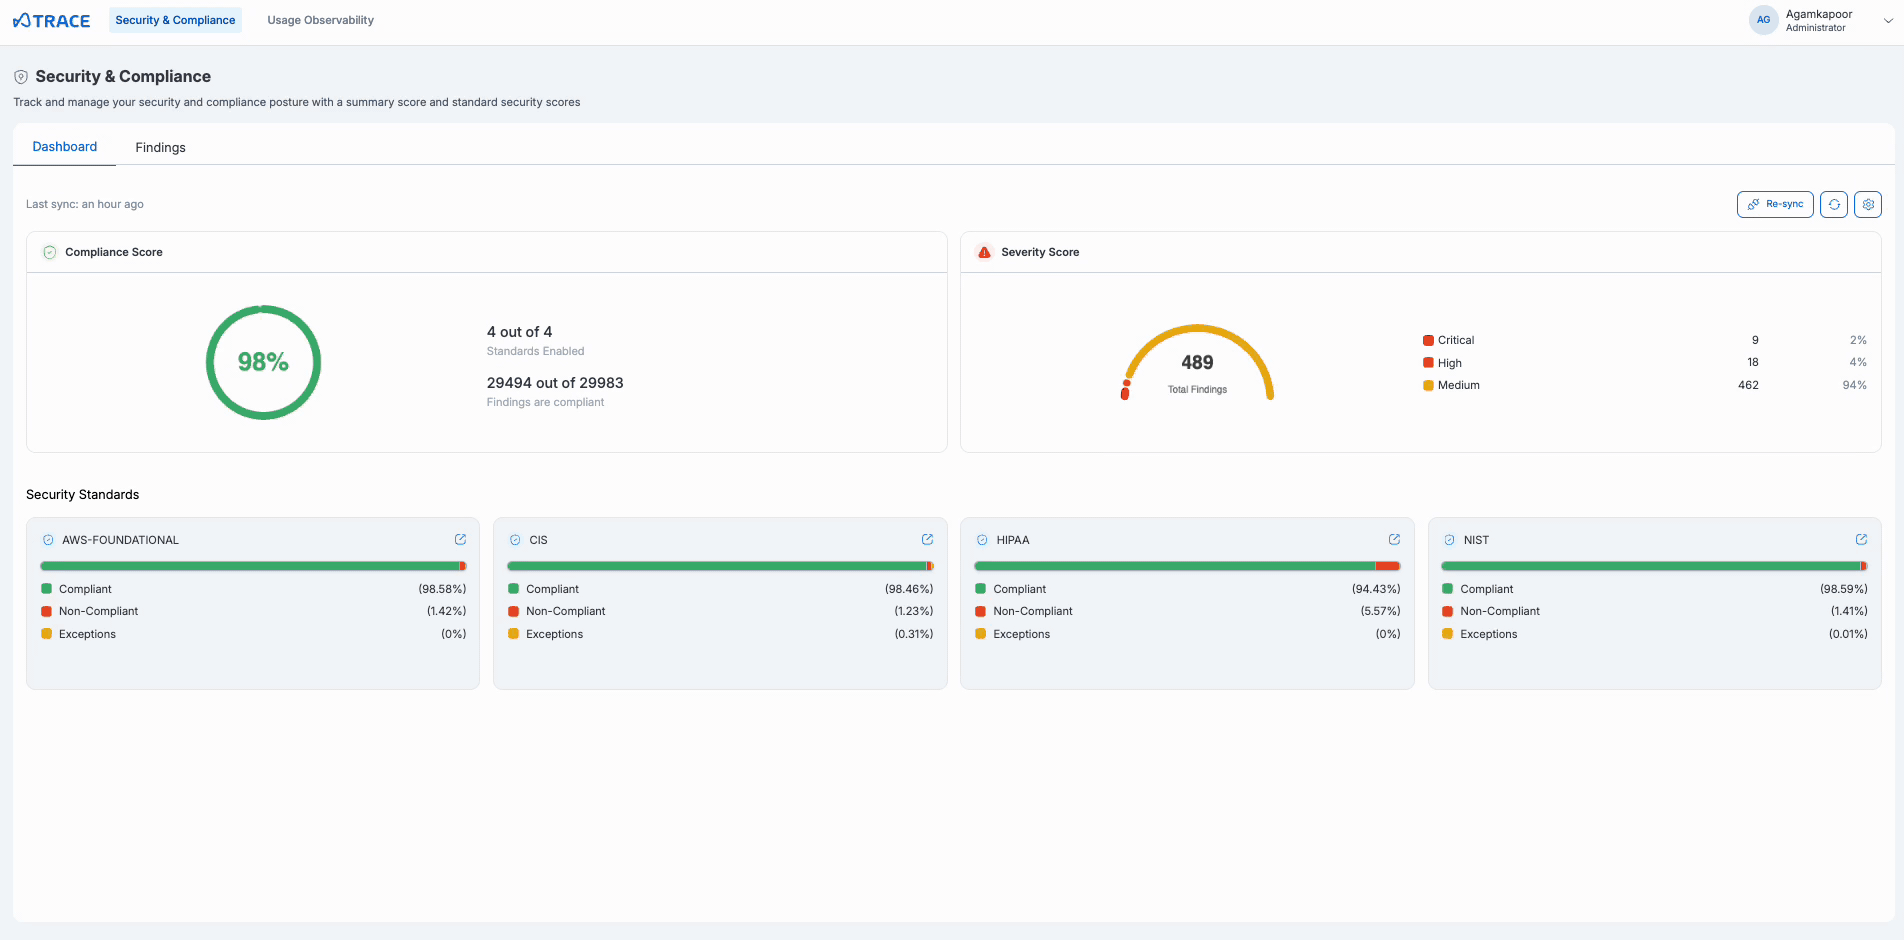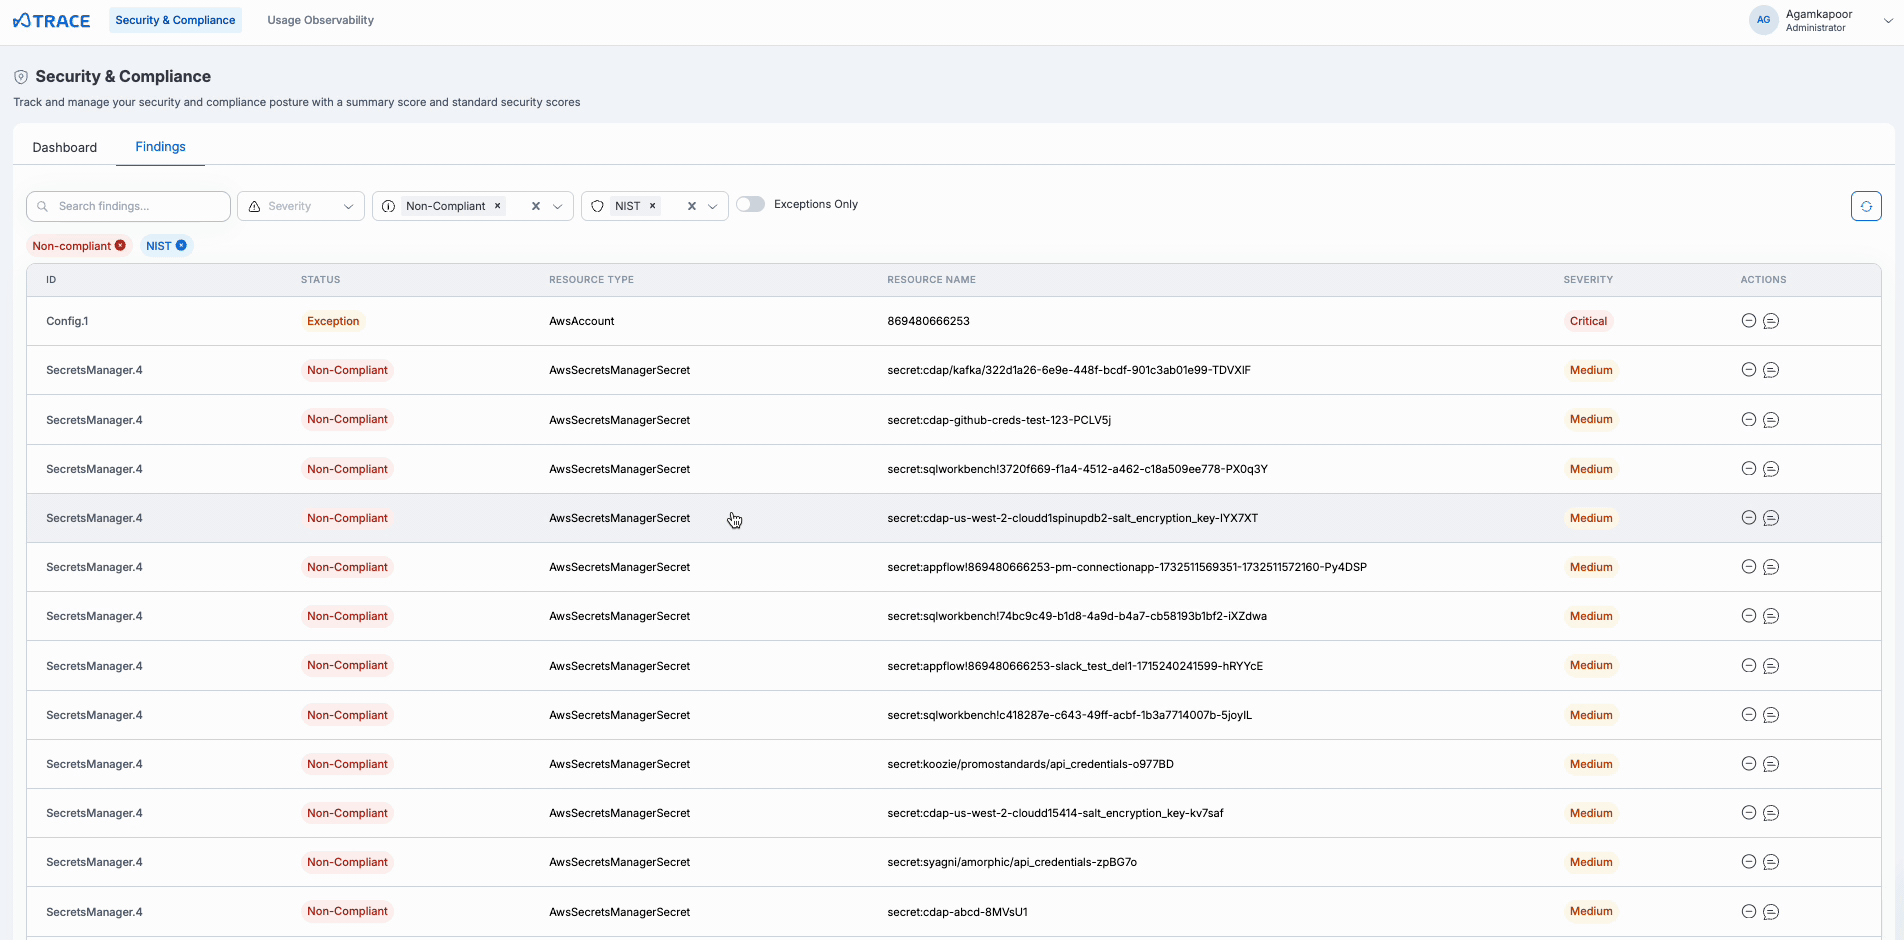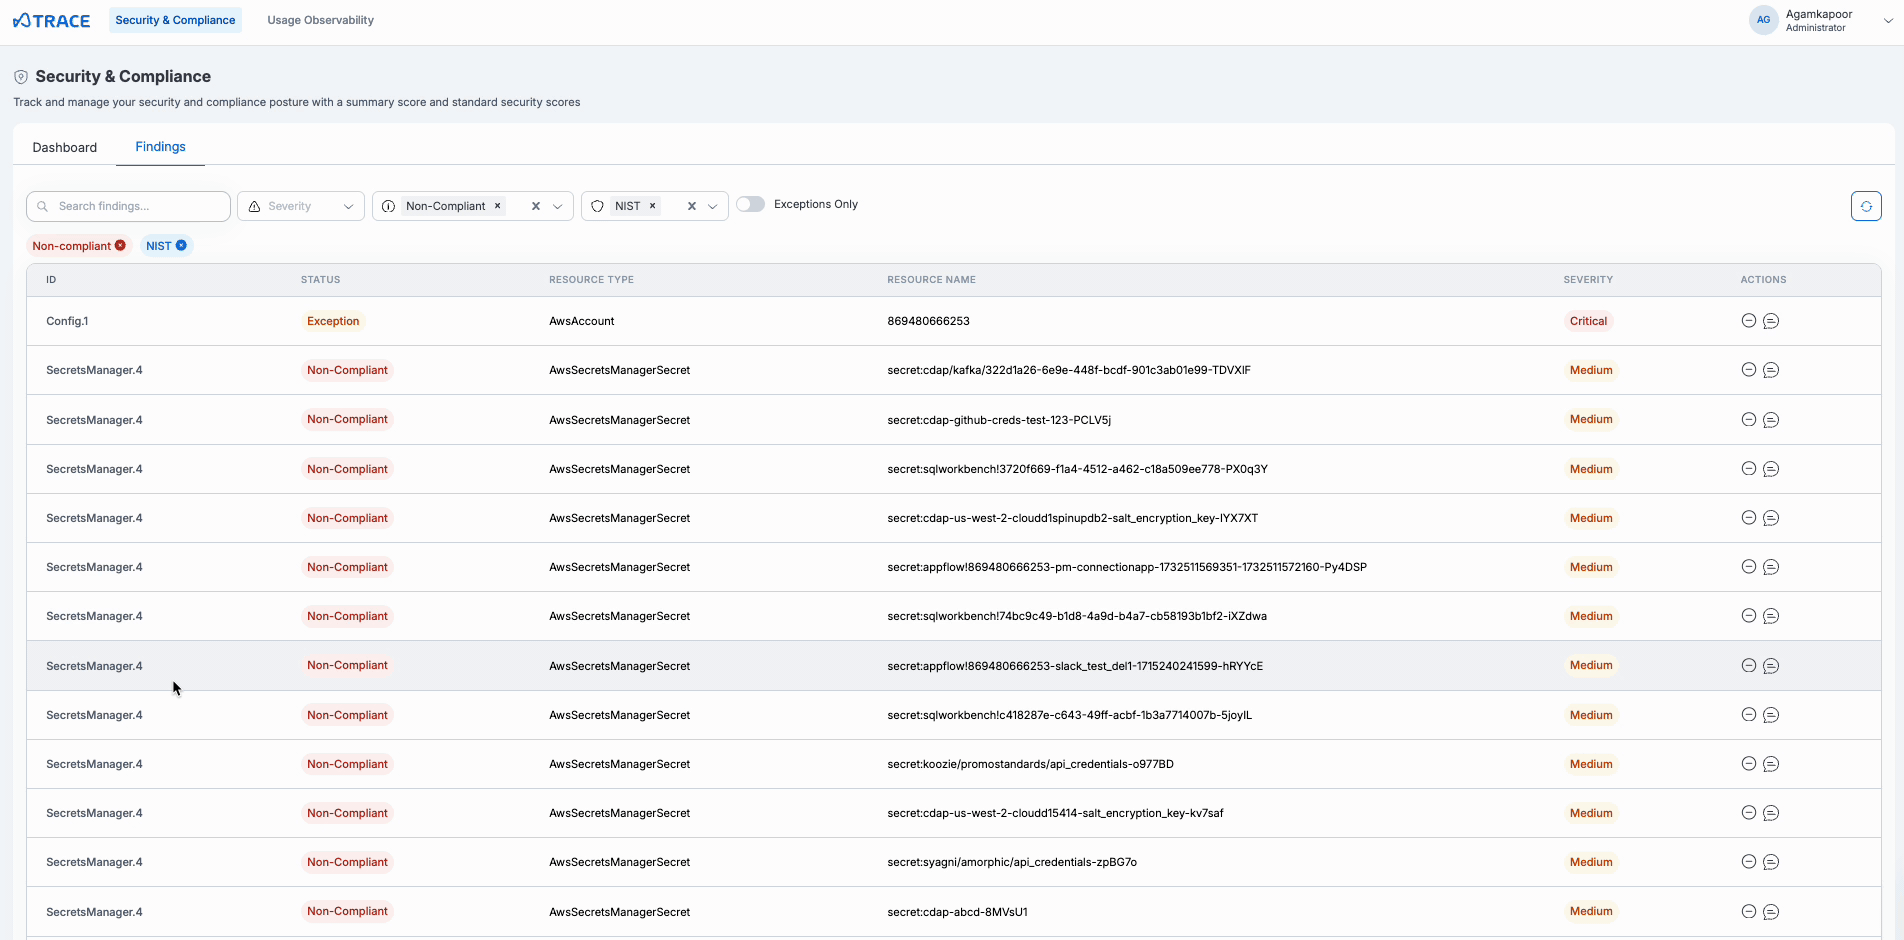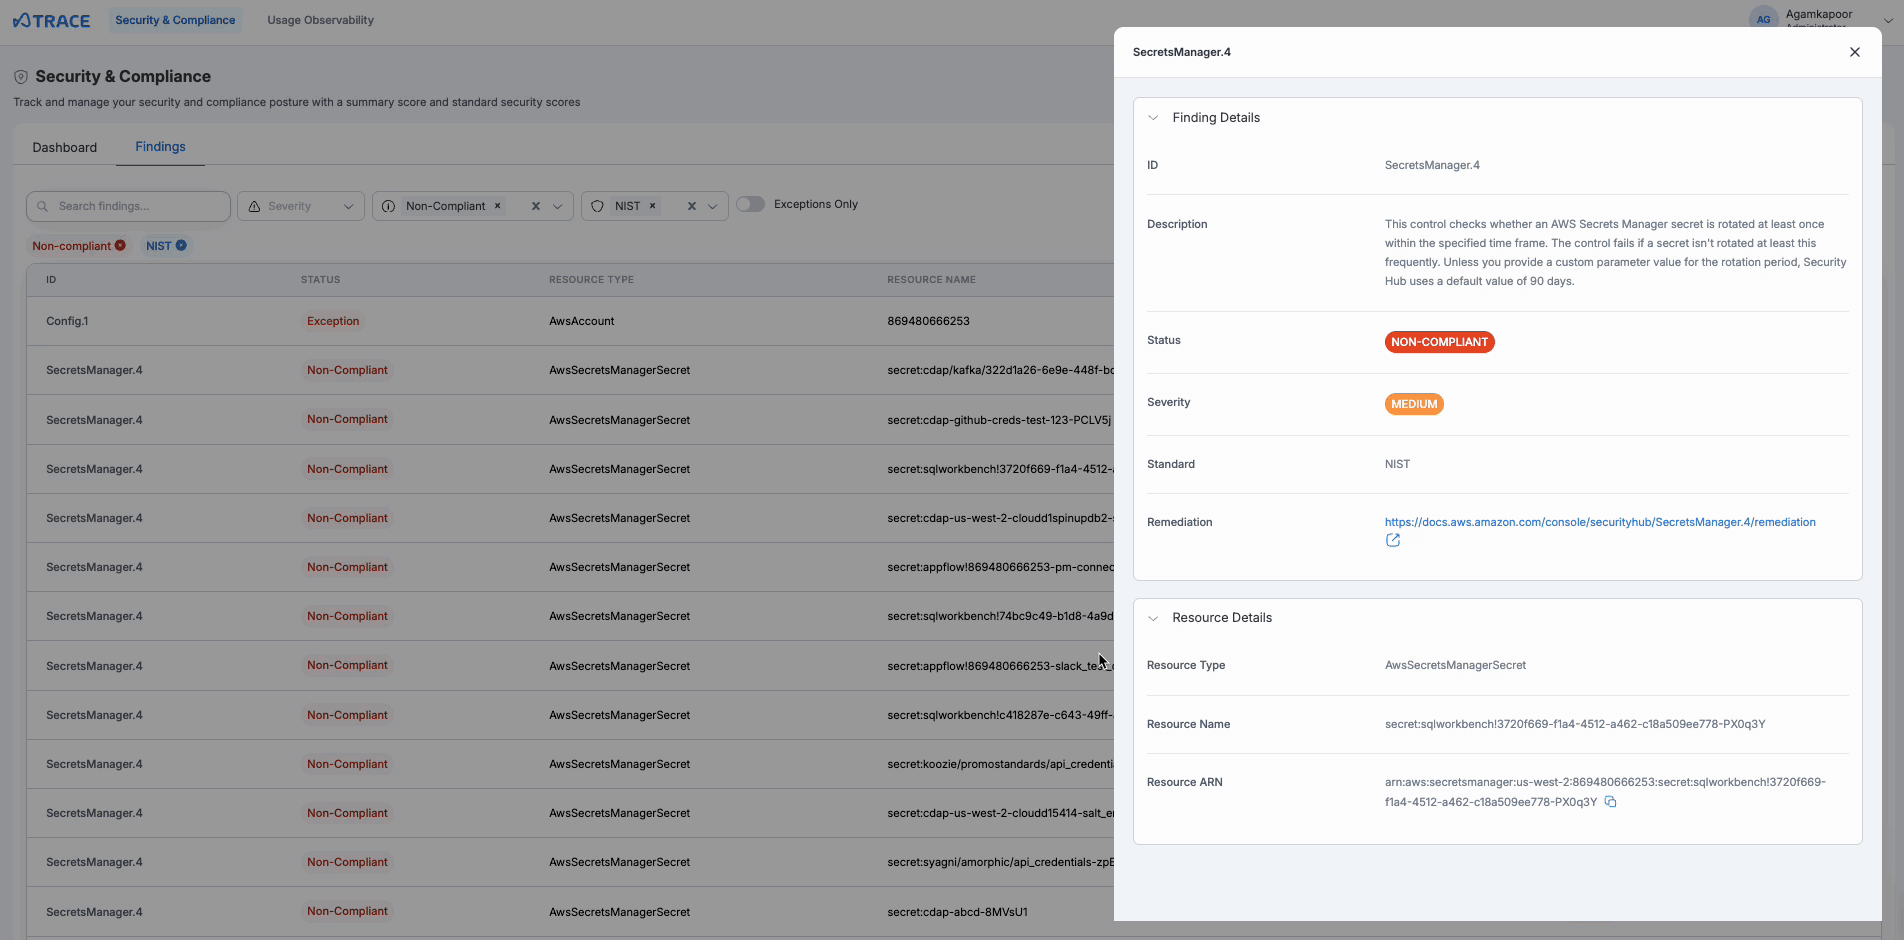
The Findings section provides detailed information about security issues:
- Finding Details: Complete description, severity, and affected resources
- Remediation Guidance: Step-by-step instructions to resolve issues
- Compliance Mapping: Which standards are affected by each finding
- Status Tracking: Current state and resolution progress
Finding Categories
Findings are categorized by severity to help prioritize remediation efforts:
- Critical: Security vulnerabilities, exposed credentials, and compliance violations requiring immediate attention
- High Priority: Infrastructure misconfigurations, access control issues, and monitoring gaps needing prompt action
- Medium/Low Priority: Best practice violations and optimization opportunities for ongoing improvement
Finding Management
Each finding provides comprehensive details including description, affected resources, severity level, and remediation steps. Users can:
- Add Comments: Document remediation efforts, business context, and track progress. A comment can be deleted by the user who added it
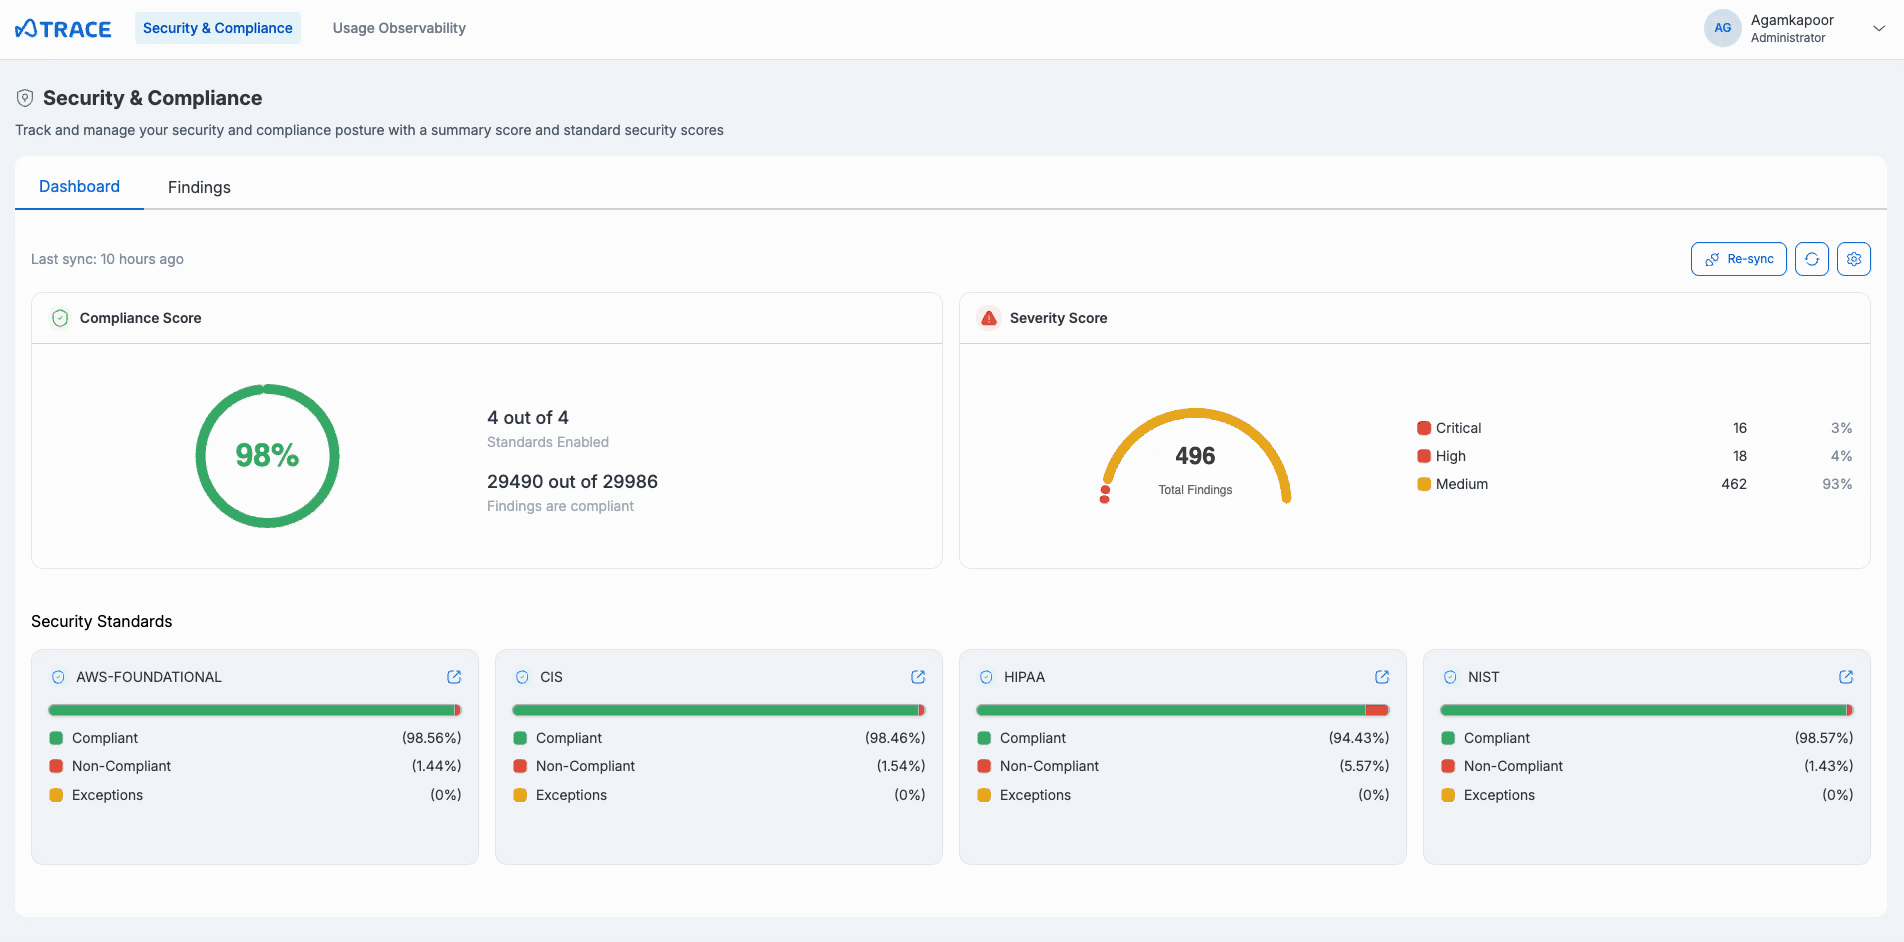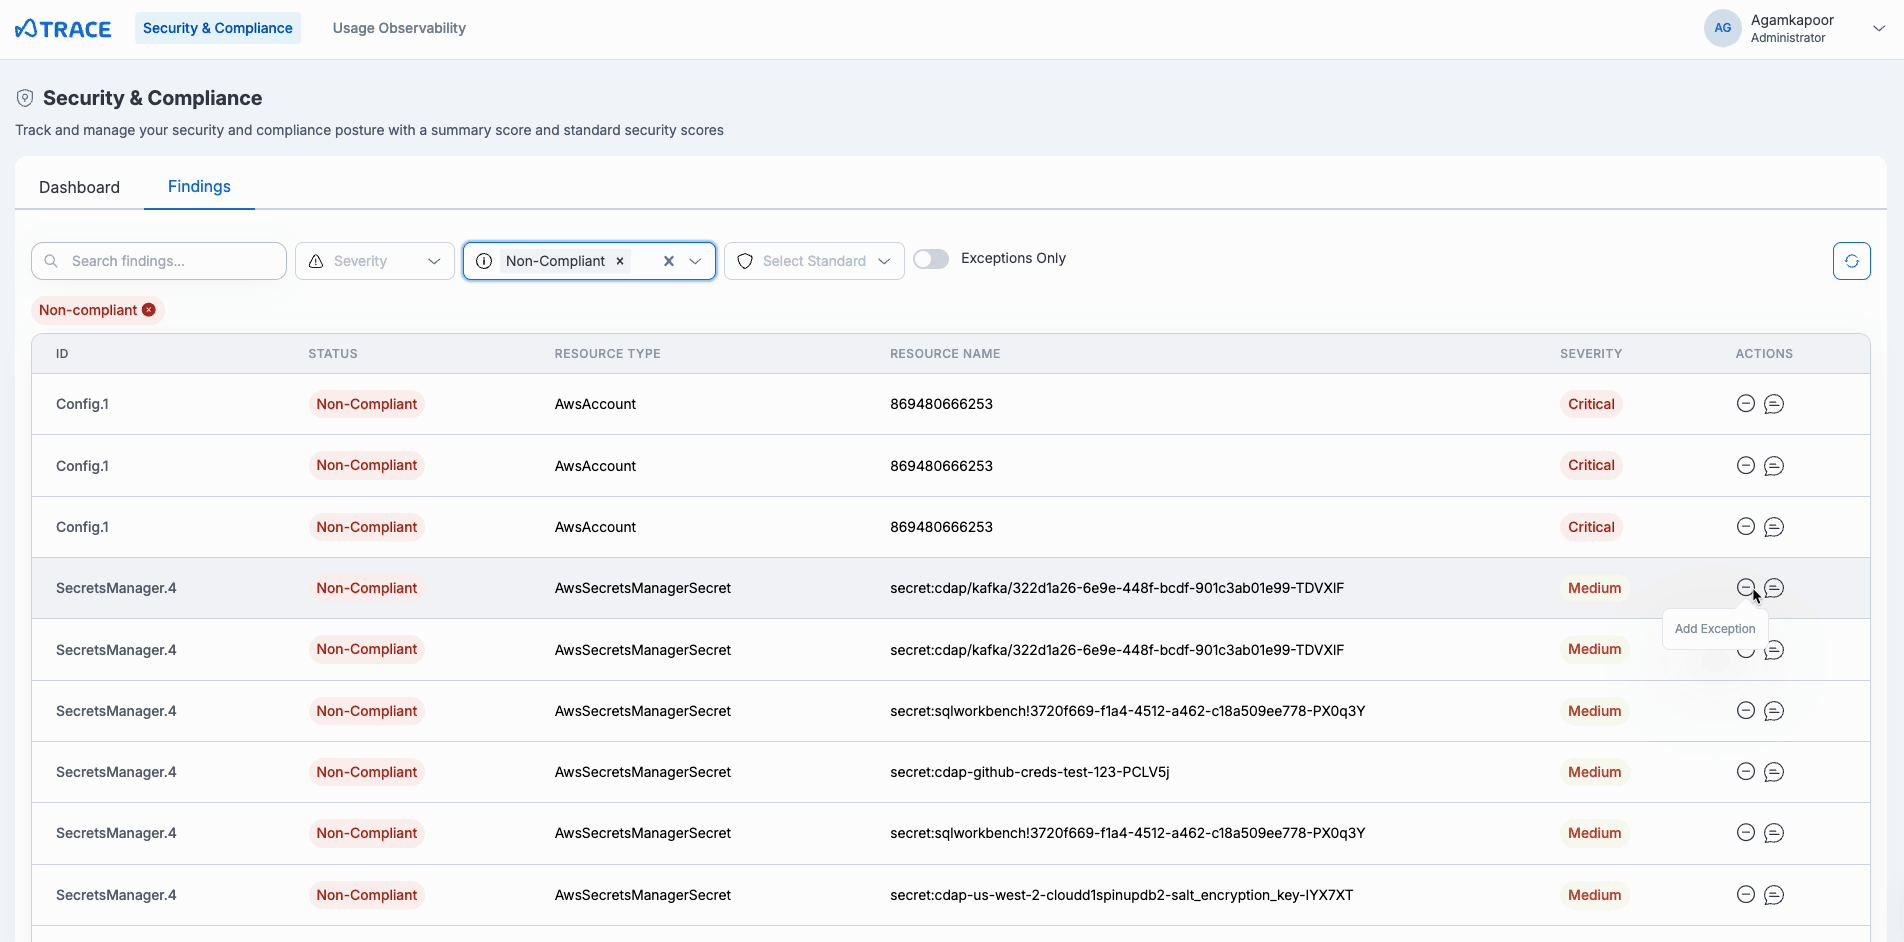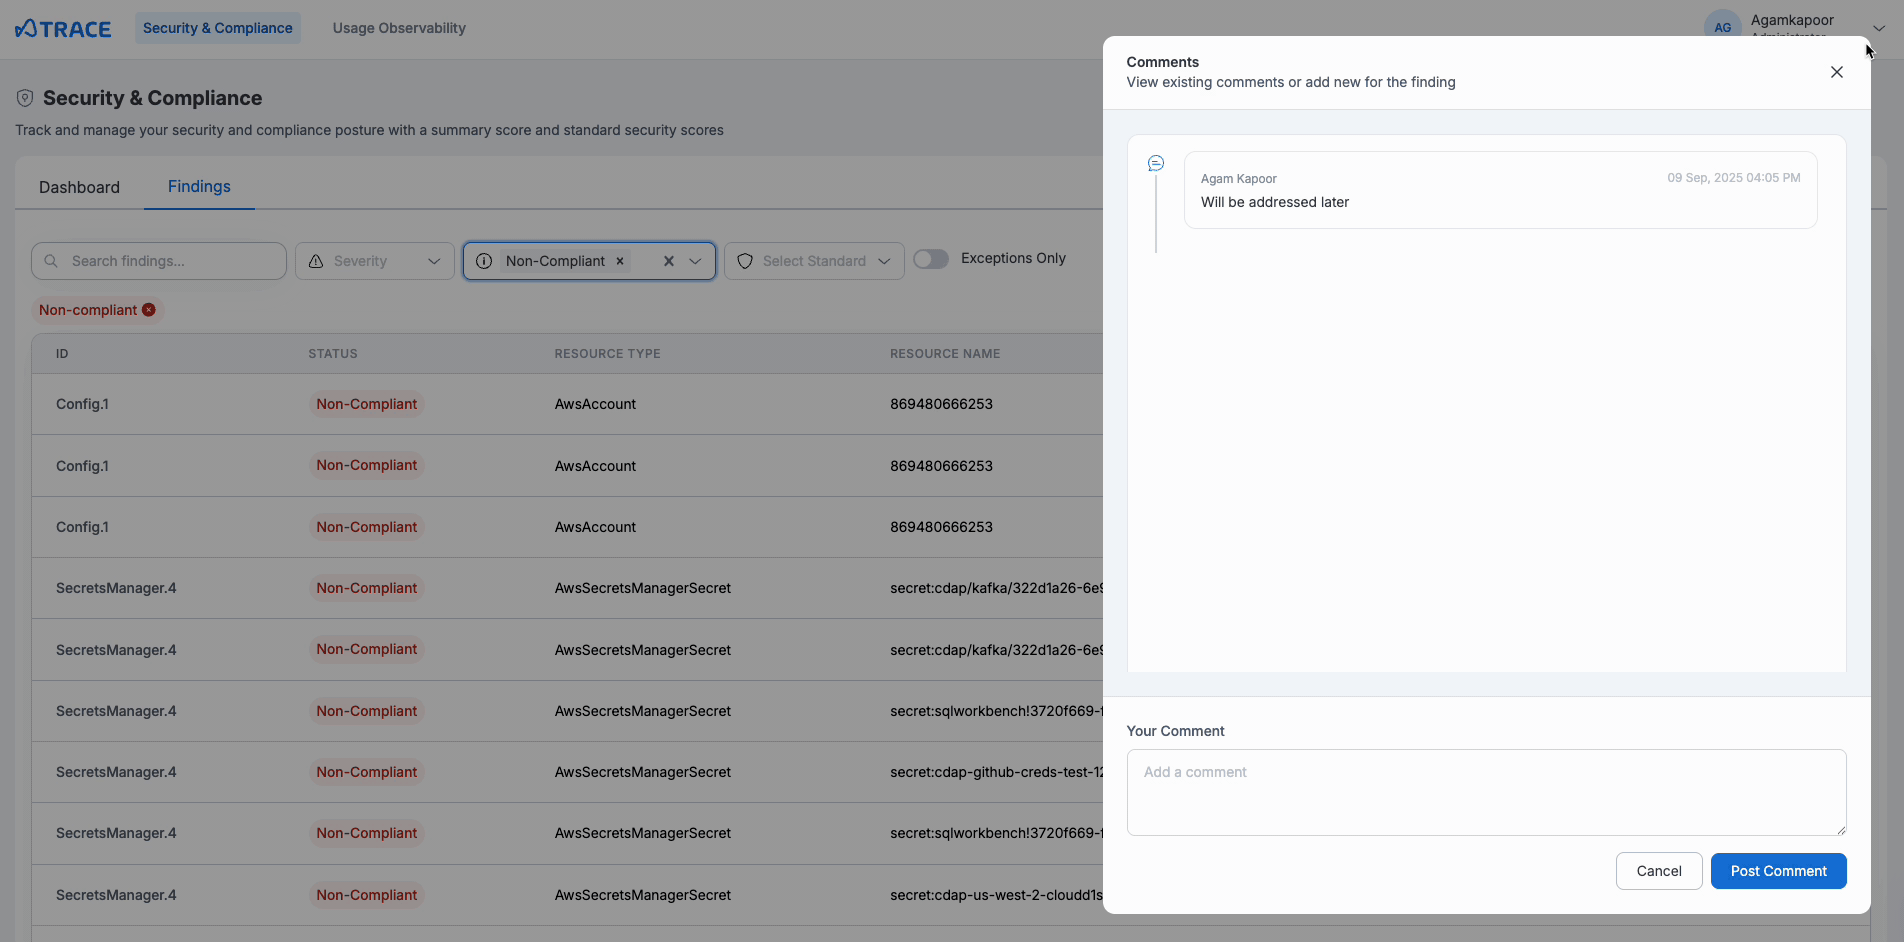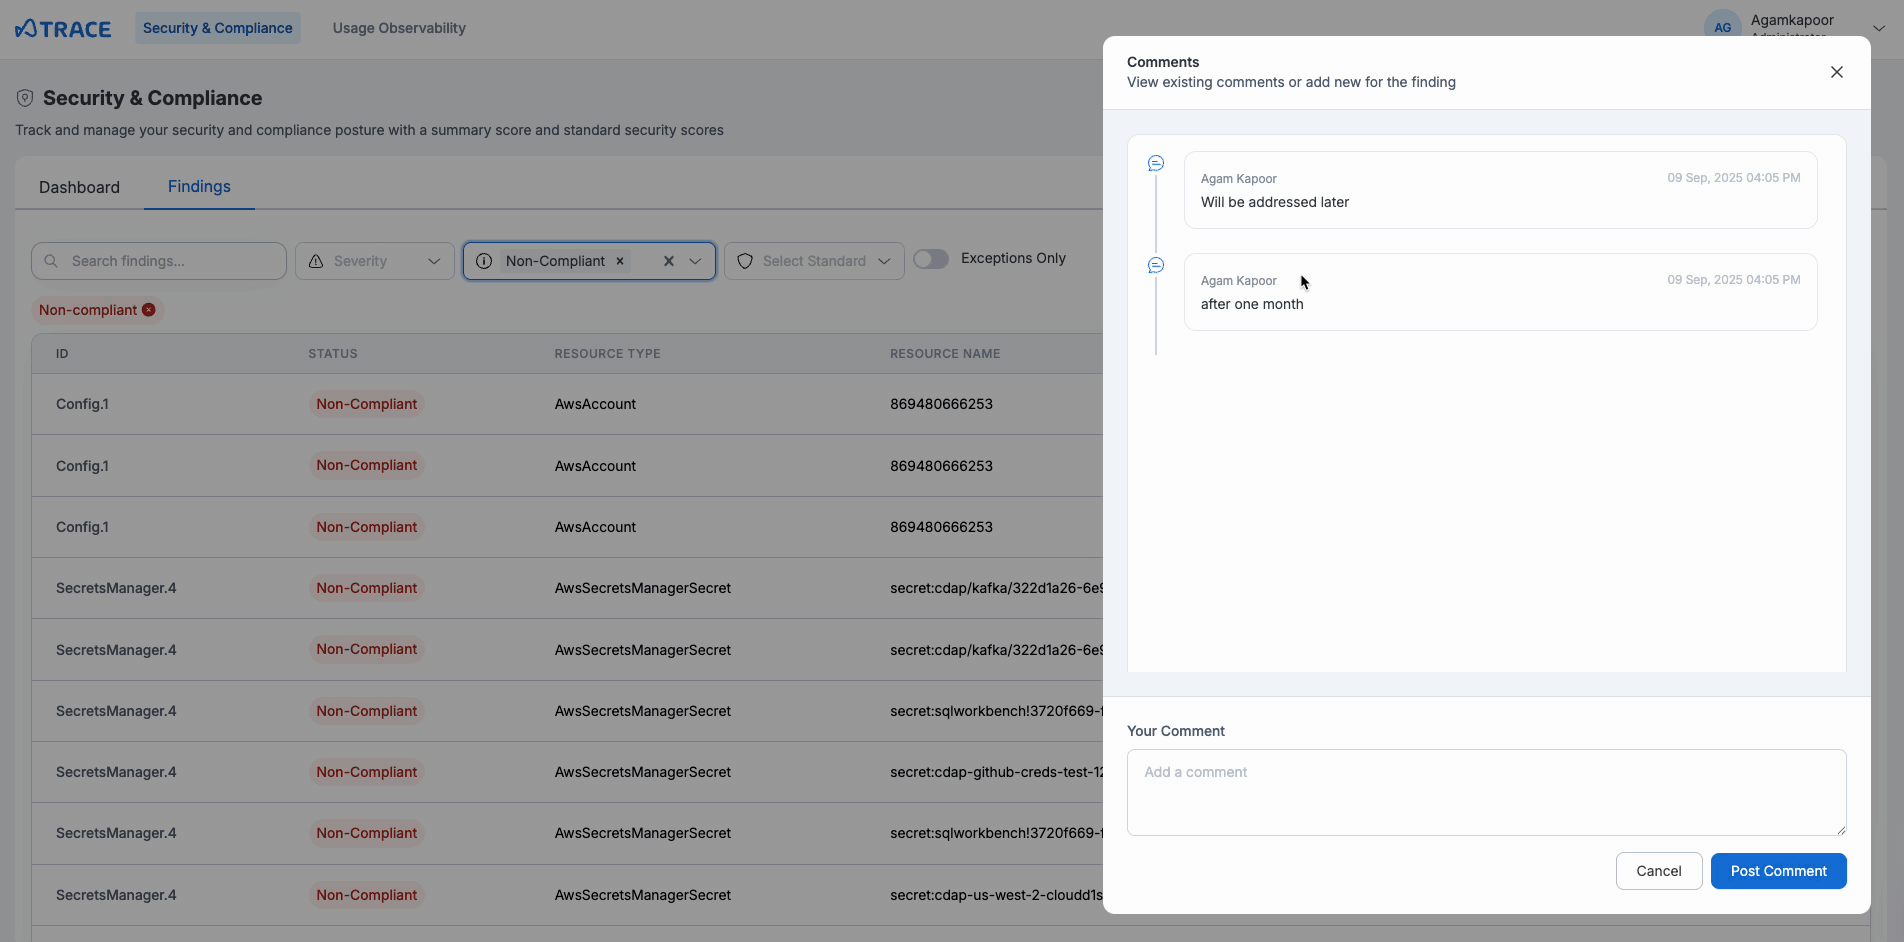
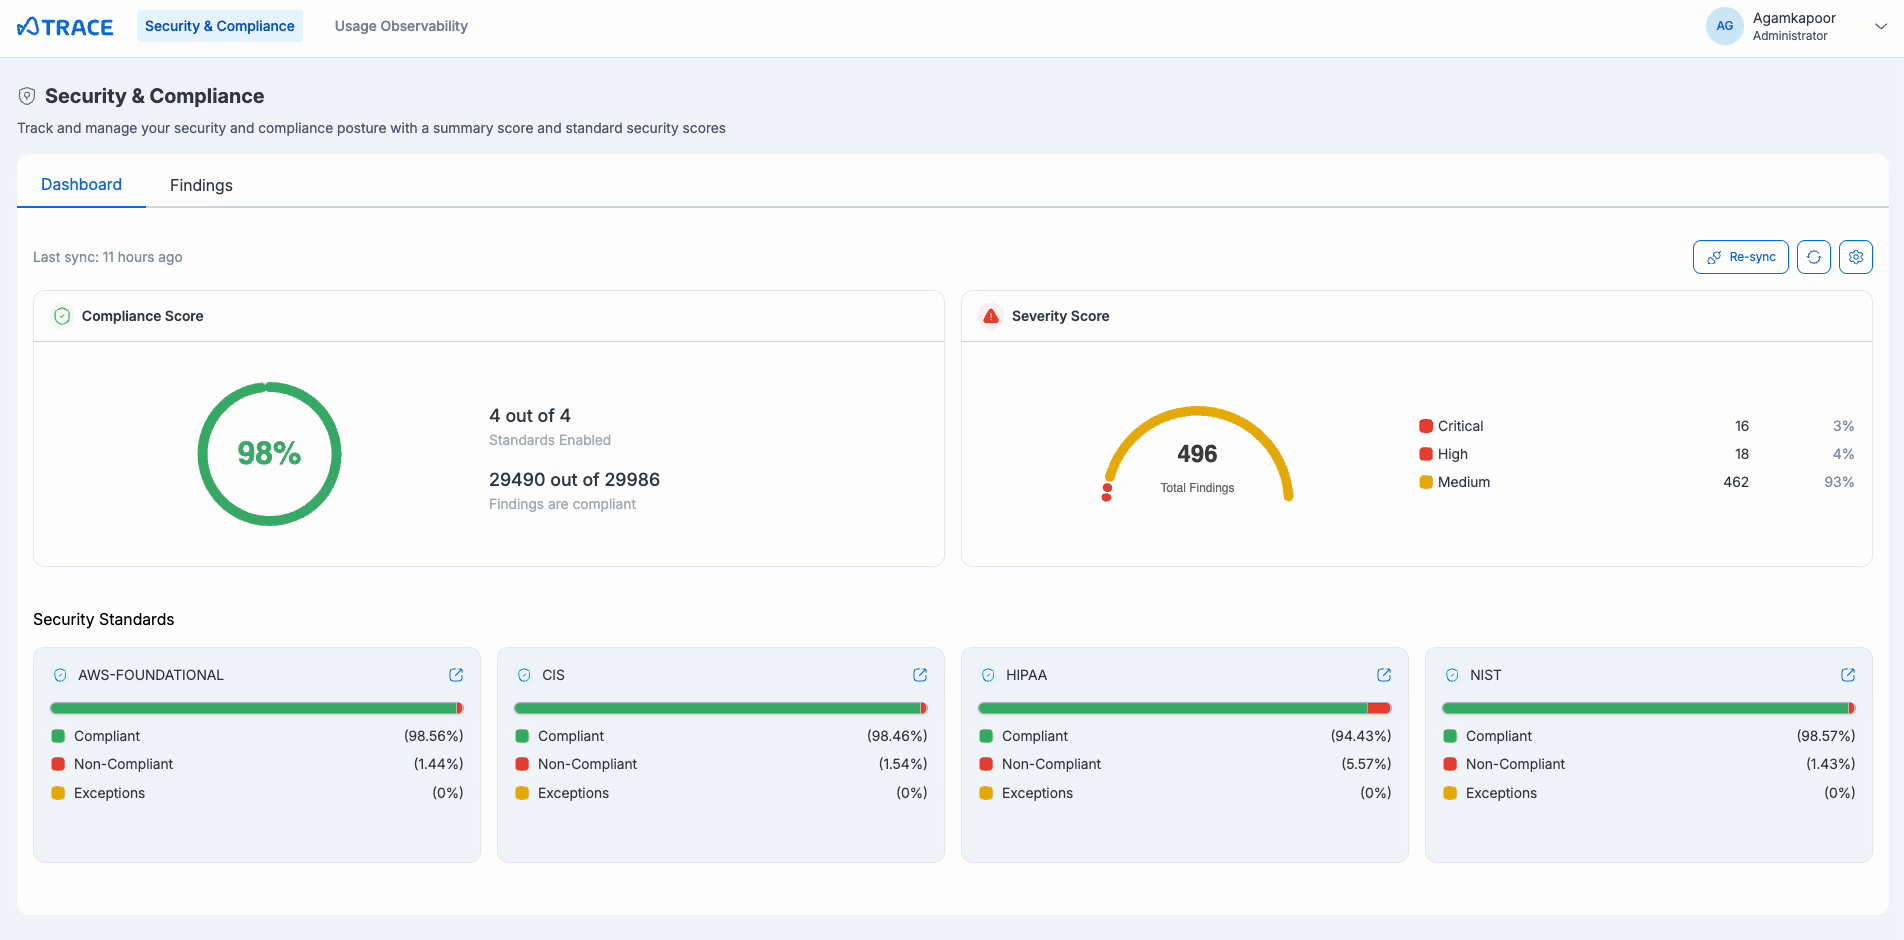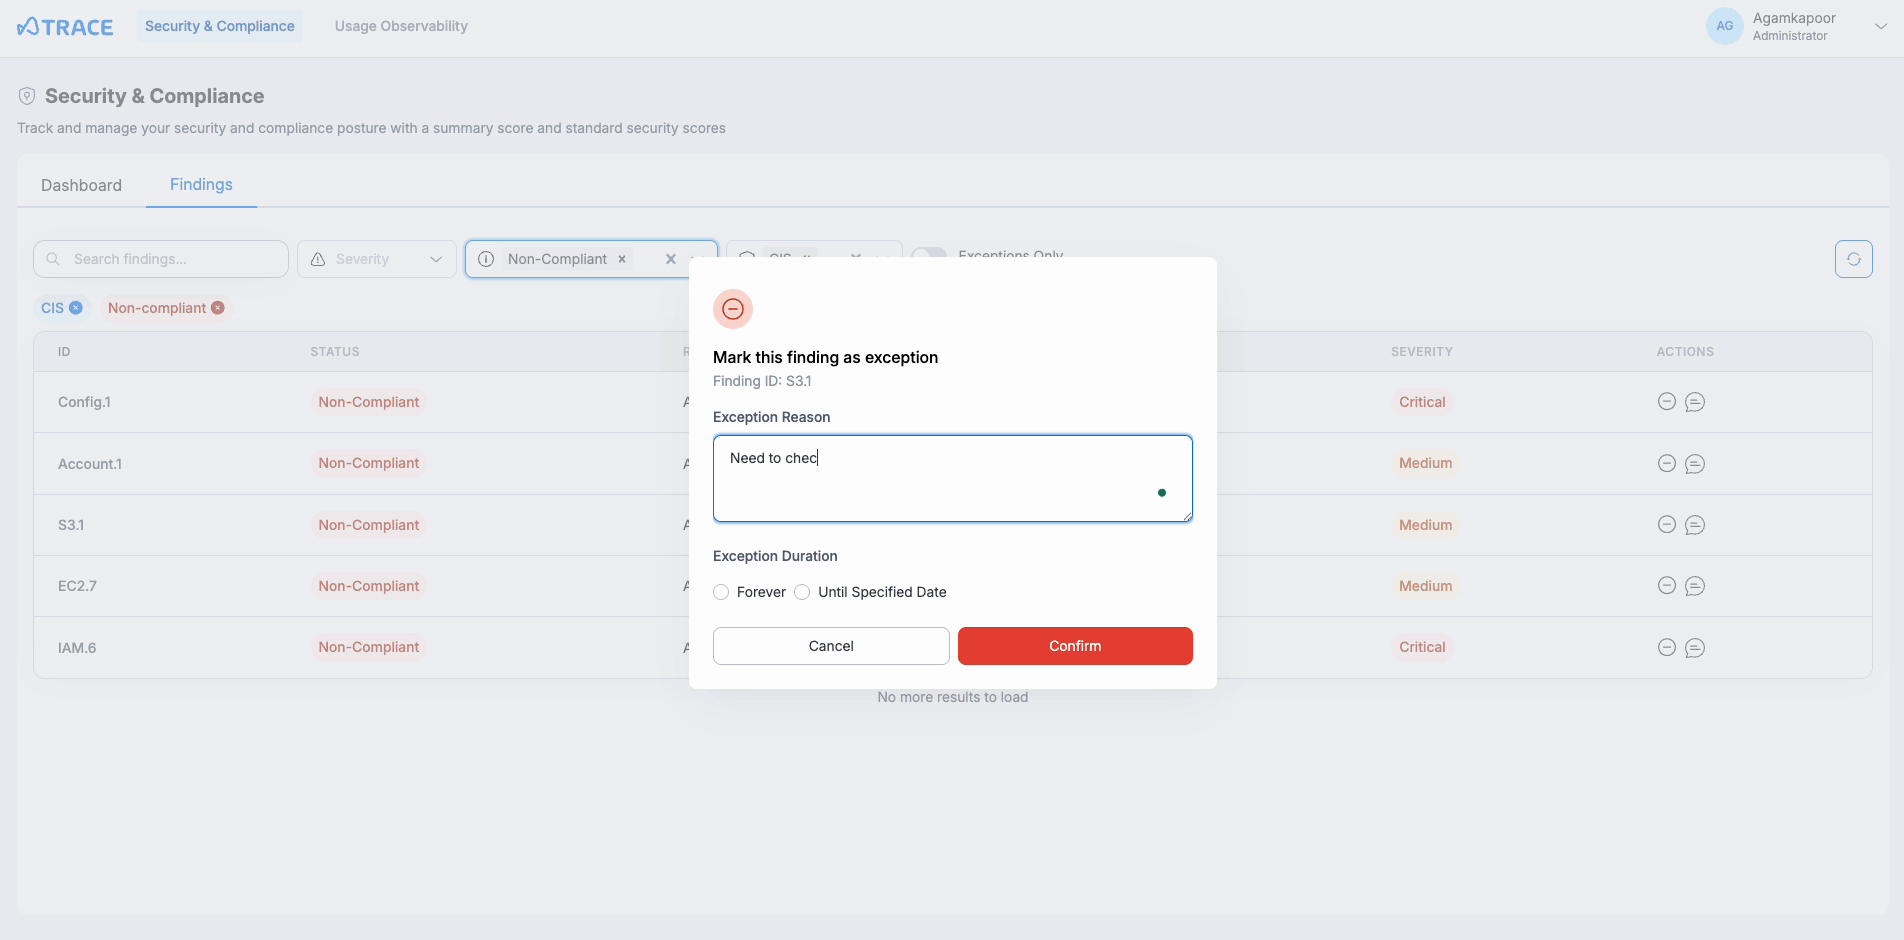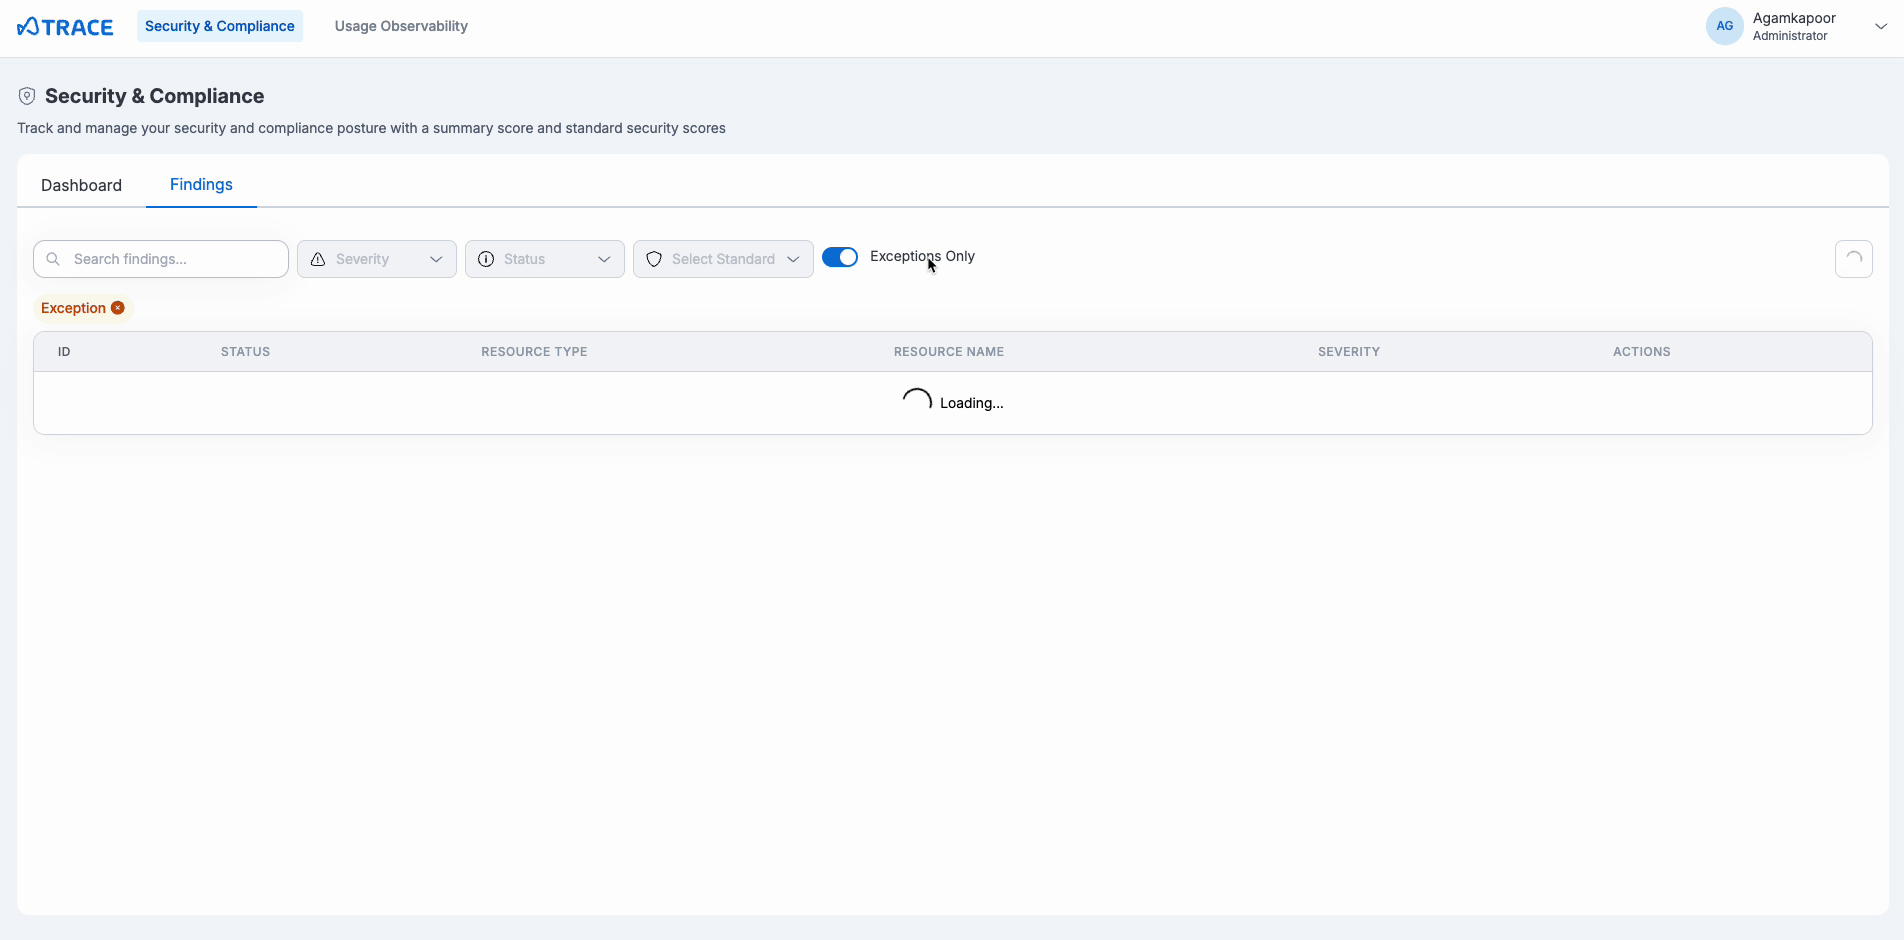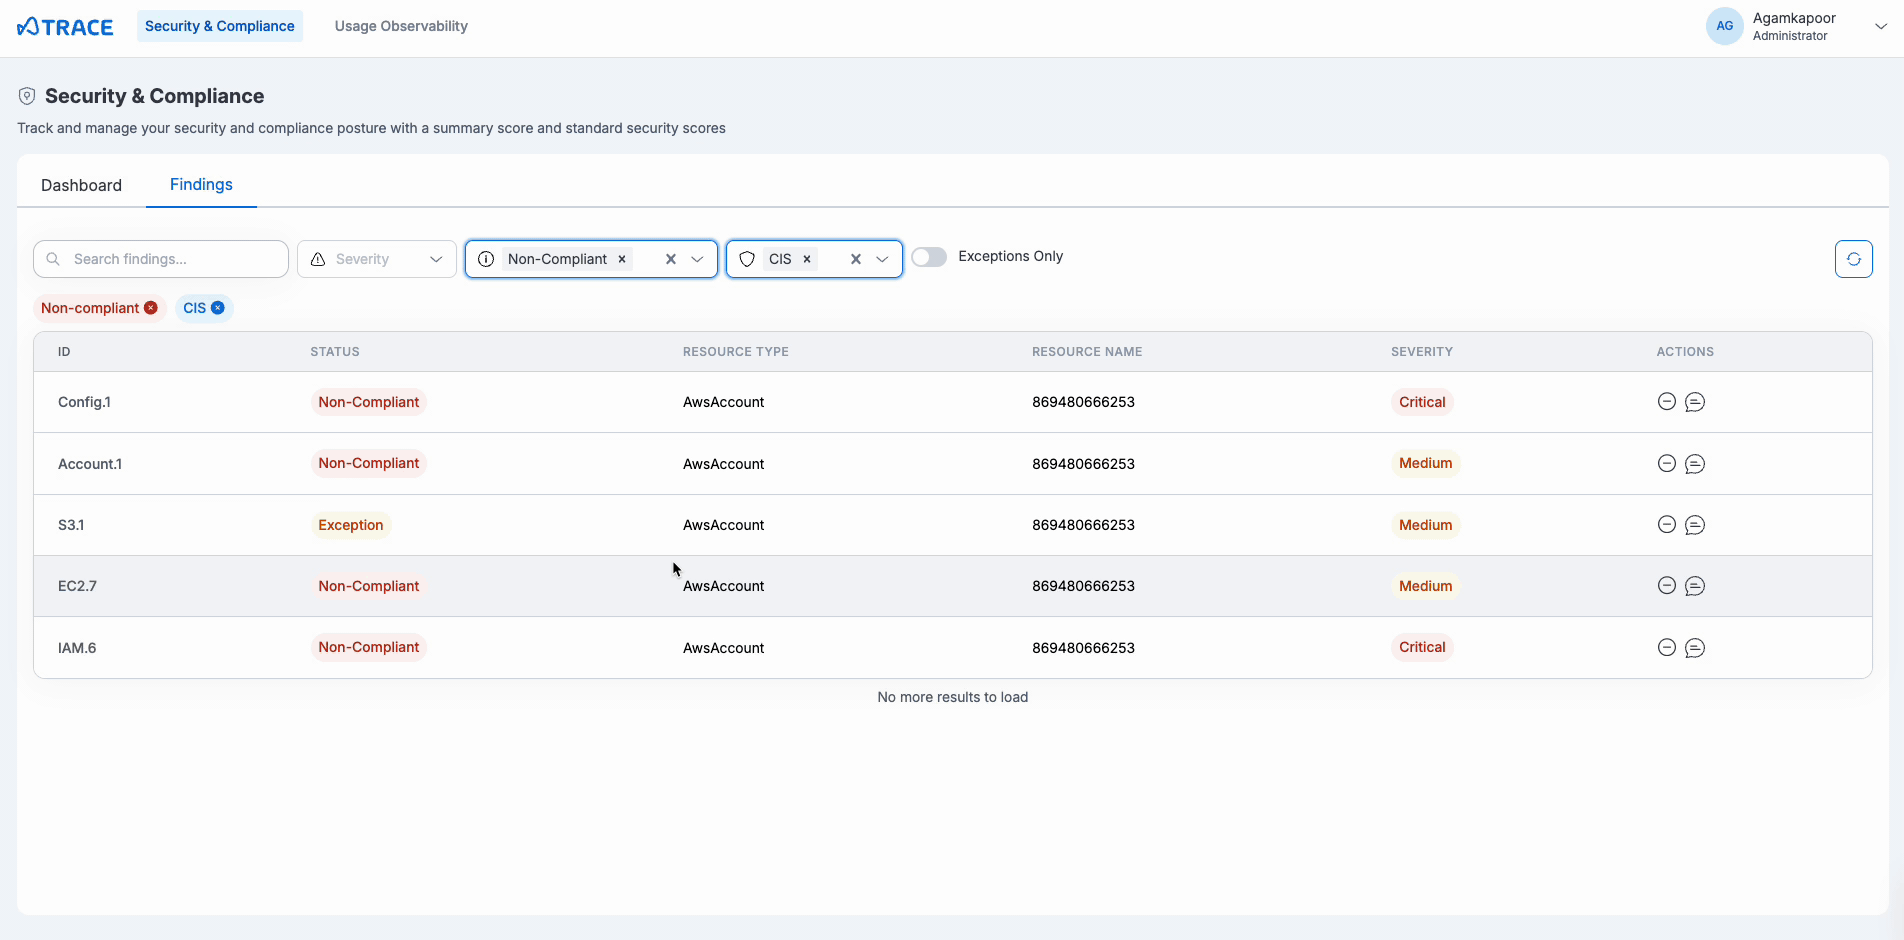
- Request Exceptions: For findings that cannot be resolved immediately or are false positives, by providing resource details, severity, and an expiration date (and remediation guidance, for non-CloudFormation standards). A written justification is optional. Exceptions take effect immediately - there is no separate approval step - and can be removed by the user who raised them, which reverts the finding to Non-Compliant
Exception Expiration
If an exception was raised with an expiration date and that date has passed, the finding status automatically reverts to the latest status from AWS Security Hub the next time compliance data is synced (scheduled or manual re-sync).